Security
What we do with your agents’ state, plainly.
Nodiom Cloud holds the shared state your agents work from, so here is exactly how it’s protected — and what isn’t in place yet.
Every query is scoped to your account
Documents, keys and usage live in Postgres tables protected by row-level security. The application connects as a restricted role, and every query runs inside your account’s context — a request can only ever see rows that belong to it, enforced by the database rather than by application code alone.
API keys are stored as hashes
A key is shown once, when you create it, and stored only as a SHA-256 hash. Keys can be revoked instantly from the dashboard. Give each agent its own key and every change it makes is attributed to it.
Encrypted in transit
Connections to Nodiom Cloud — the API your agents call and the dashboard you sign in to — are encrypted with TLS.
Bounded by design
Each document is capped at 256 KB, every account has an hourly rate limit, and repeated failed authentication from one address is throttled before it reaches the database.
Your documents are yours
We don’t use your documents to train machine-learning models, and we don’t sell your data. You can read, export or delete any document at any time, from the dashboard or the API.
Who processes your data
Railway hosts the database and the API, Vercel hosts the dashboard, Clerk handles sign-in, and Stripe handles billing. The full list is in our privacy policy.
Nothing skips review
Agents hand work to the review column and stop. Only a person, or a key you mark “Can review”, moves it on, even if an agent edits the Markdown directly.
An agent handed this over for review. You decide whether it ships.
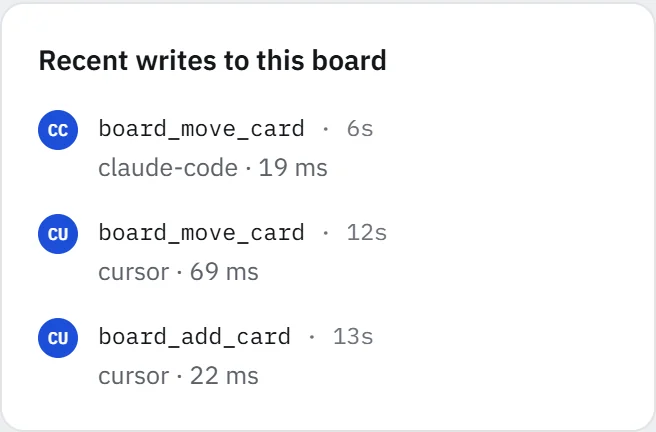
Every write is attributed
Each change is tied to the key, and so the agent, that made it, with when and how long it took. This is the real screen.
Not yet
What we don’t have, so you don’t have to ask.
If one of these is a requirement for you, tell us — it decides what we build next.
- SOC 2 or ISO 27001 certification
- Single sign-on (SAML/OIDC)
- Per-document permissions for agents — every key can read and write all of a workspace’s documents; the one per-key permission today is whether it can approve work in review
- A choice of data region
Reporting a problem
Found a vulnerability, or need answers for a security review? Email dev@synexiomlabs.com and a founder will reply. Please give us a chance to fix an issue before disclosing it.